 United States
 United Kingdom
 Canada
 Australia
 New Zealand
 Ireland
Low Level traces SSH login flaw to a single asterisk
His explainer shows how an overlong password could unlock access on specific Linux setups, without a buffer overflow.
 Low Level
Story of
Why this story? 929,836 views so far, and here is what is inside it.
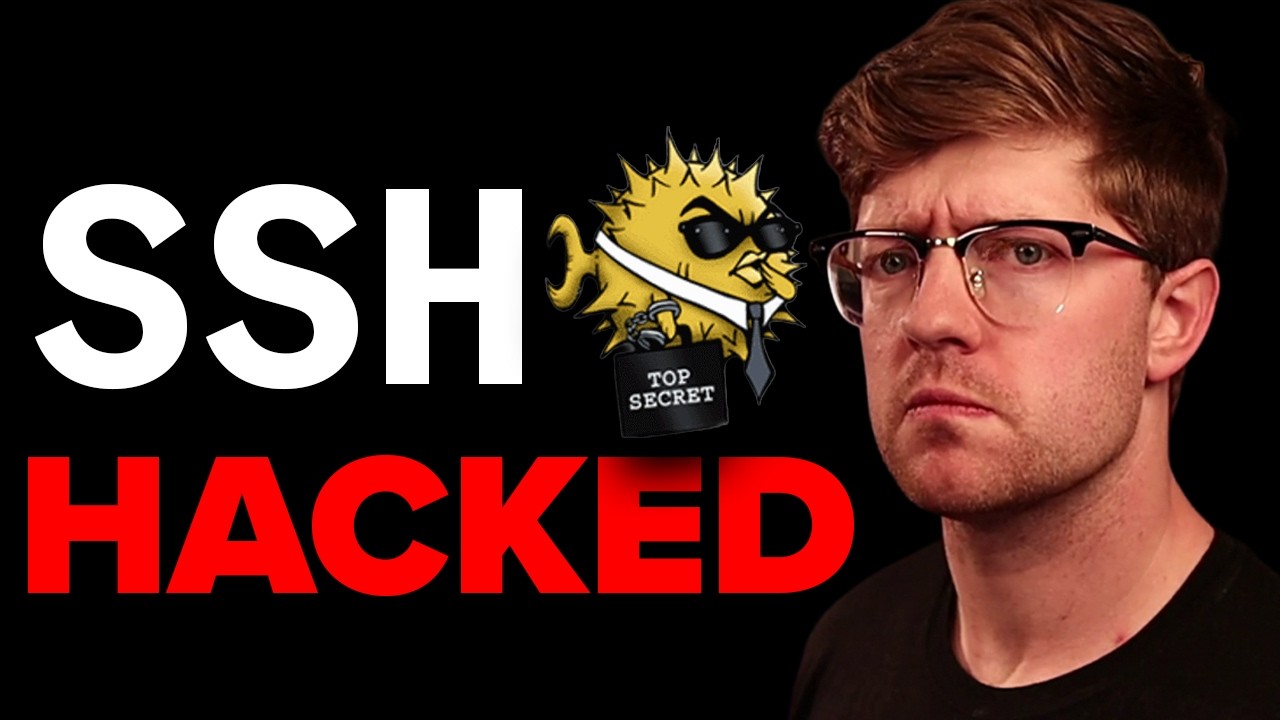 SSH situation is insane
Things we can learn from the video
Press to jump
- 0:57An overlong password could grant root access on affected systems; this is not a buffer overflow.
- 3:32An asterisk in a stored password entry can indicate that password login is disabled.
- 4:47Musl's hashing function changed its error result from NULL to an asterisk, creating a dangerous overlap.
- 7:52Exceeding the password-length limit returns an asterisk that can match the locked account's entry.
- 8:48Exploitation requires specific conditions, including a musl-based OpenSSH server build without PAM authentication modules.
- 12:35Memory-safe languages would not automatically prevent this flaw because it is a logic error.
How can a password nobody chose pass a login check? In Low Level's "SSH situation is insane," the answer is an error message that accidentally looks exactly like a locked account's stored password entry.
The host examines a vulnerability discovered by researcher Özgün Kültekin. Under specific conditions, entering a password longer than 256 characters could grant unauthorized root access, the powerful administrator account on a Linux system.
The surprising part is not that the long input overwrites memory. "It is not a buffer overflow," he says. Instead, separate pieces of software make assumptions that become dangerous when combined.
An asterisk in the system's password records can mark an account as unavailable for password login. But the musl software library's password-hashing function also returns an asterisk when it encounters certain errors. Feed it an excessively long password, and the failure result can match the very entry intended to keep the account locked.
Low Level walks through the additional SSH logic that makes that match possible, then narrows the scope: this affects particular musl-based OpenSSH server builds without PAM authentication modules, including affected Alpine Linux configurations. It is not a claim that every SSH server accepts a very long password.
The video, which includes a sponsored segment for a threat-intelligence service, has drawn nearly a million views. Viewers turn the password-length absurdity into jokes, while others debate whether a conspicuous software failure would have been safer than returning an ordinary-looking value.
Near the end, Low Level addresses the inevitable Rust question. A memory-safe language would not automatically solve this one: the mistake is in the logic deciding whether authentication succeeded.
Published on Trari
Where next?


What viewers say
Think if your password was 300 characters and you just blast that thing in 100% correct every time and then you find out it was just a bug.
@Monster_RancherSee it on YouTube"Worst password hash ever - one star." 😆
@simond.455See it on YouTubeInterviewer: "how did you find this bug? it must have taken a lot of research."
Researcher: "my cat sat on the keyboard, and when he got up, I hit enter to clear the buffer... and it logged me in."@chaos_ensuedSee it on YouTube
2 more comments
I agree with everything said in this 13 minute video that was posted 1 minute ago.
@FrankLeesonSee it on YouTubeThey should have kept the NULL return value. "But then programs that don't handle the return value correctly crash." Good! Let them crash *loudly*! Then the devs notice and fix it. It's a DoS, but not an auth bypass.
@bloody_albatrossSee it on YouTube
Public comments from the video's page on YouTube
 Is this your channel?For the channel's owners and team: a ready picture and text for your audience
Share the story with your audience. Everything is ready:
For an Instagram story or a WhatsApp status
For a community post or your channel's description
- Channel
- Low Level
- Subscribers
- 1,200,000
- Channel views, last 7 days
- 2,185,992
- Channel views, pace per day
- 102,725 (on a normal day: 427,826)
- Video published
- November 6, 2026
- Video views so far
- 929,836 (3 days online)
- Video views, pace per day
- 89,068 (on a normal day: 176,127)
The numbers
The explainer has reached a substantial audience, though its views are not unusually high for Low Level.
💡 Test your knowledge
What is the traditional name of Linux's all-powerful administrator account?
The root account has administrative privileges across a Linux system.