 United States
 United Kingdom
 Canada
 Australia
 New Zealand
 Ireland
Low Level explains PHP's memory bug and incomplete fix
A cats-and-dogs code example makes the vulnerability understandable, before the report turns to questions about the patch.
 Low Level
Story of
Why this story? 1,367,713 views so far, and here is what is inside it.
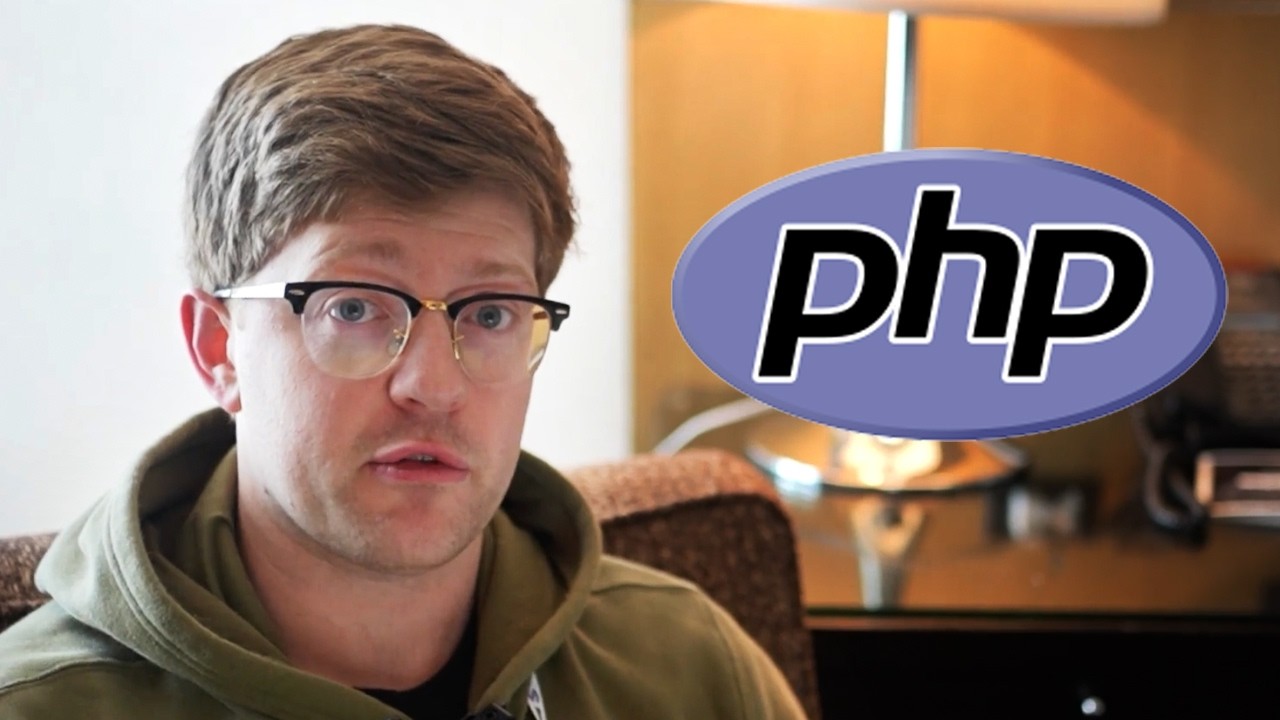 php situation is insane
Things we can learn from the video
Press to jump
- 2:51PHP supports widely used platforms including WordPress, Drupal, Laravel and Nextcloud, explaining the potential reach of a runtime flaw.
- 3:16A memory-allocation failure during file uploads can leave the program using memory it has already freed.
- 6:14Cat and dog structures in C illustrate how a use-after-free bug can lead to unintended code execution.
- 8:18Low Level describes researchers using language models to find bugs involving when memory is used and released.
- 9:03Reports of double-free errors after the official patch raise questions about whether the repair is complete.
Low Level reaches for cats and dogs to explain how a file-upload bug could let an outsider run code on a web server. The animals are structures in a C programming example, a way into the memory-management problem behind "php situation is insane".
Reporting from a Las Vegas hotel room while attending SentinelOne's OneCon event, the host describes a flaw in PHP, the software underpinning sites and applications built with tools such as WordPress, Drupal and Laravel. He says the bug has been sitting in the code for more than two decades.
The explanation gets concrete: when memory allocation fails during file-upload handling, the program can end up using memory it has already released. That is a "use-after-free" bug. His example shows how reusing that space for something else can turn a stale reference into a route to unintended code execution.
Finding the flaw is only part of this report. Low Level describes researchers using large language models to uncover bugs involving the lifetime of objects in memory. He then examines social media reports showing that the official patch still produces double-free errors, where software tries to release the same memory twice. His concern is not simply that a fix was needed, but that the first fix may not finish the job.
The video has reached about 1.4 million views in three days. In the comments, the technical discussion shares space with a recurring joke: major internet problems seem to wait until Low Level is away from home.
Published on Trari
Where next?

What viewers say
STOP GOING ON VACATION, THE INTERNET KEEPS BREAKING WHEN YOU LEAVE
@sampellinoSee it on YouTubemysteriously in a hotel every time something like this happens
@hri7566See it on YouTubeAI has become Internet’s LockPickingLawyer.
@keyserzoom9154See it on YouTube
3 more comments
Who else here was waiting for Low Level’s take on this?
@YouthureSee it on YouTubeWork in Patch Management
This one broke me in one day with all the customers shouting for a quick fix@gagans8654See it on YouTubeI've been eagerly waiting for this video. Your explanations of exploits and vulnerabilities are always fun and informative. I also know that you will never see this comment, because somehow there are 80 comments already, only 20 minutes after you posted it.
But anyway, keep up the good work!@fighterguardSee it on YouTube
Public comments from the video's page on YouTube
 Is this your channel?For the channel's owners and team: a ready picture and text for your audience
Share the story with your audience. Everything is ready:
For an Instagram story or a WhatsApp status
For a community post or your channel's description
- Channel
- Low Level
- Subscribers
- 1,190,000 ▲ 10,000 this week
- Channel views, last 7 days
- 4,980,782
- Channel views, pace per day
- 196,462 (on a normal day: 563,805)
- Video published
- October 22, 2026
- Video views so far
- 1,367,713 (3 days online)
- Video views, pace per day
- 147,549 (on a normal day: 617,635)
The numbers
The PHP report has passed a million views. Here is how its audience sits alongside Low Level's wider channel activity.
💡 Test your knowledge
What does RCE stand for in cybersecurity?
RCE means remote code execution, allowing code to run on a system from elsewhere.